Kubron brings everyday Kubernetes operations into one workspace across desktop and web: inspect cluster health, understand what changed, troubleshoot issues and take action without switching between a dozen tools.
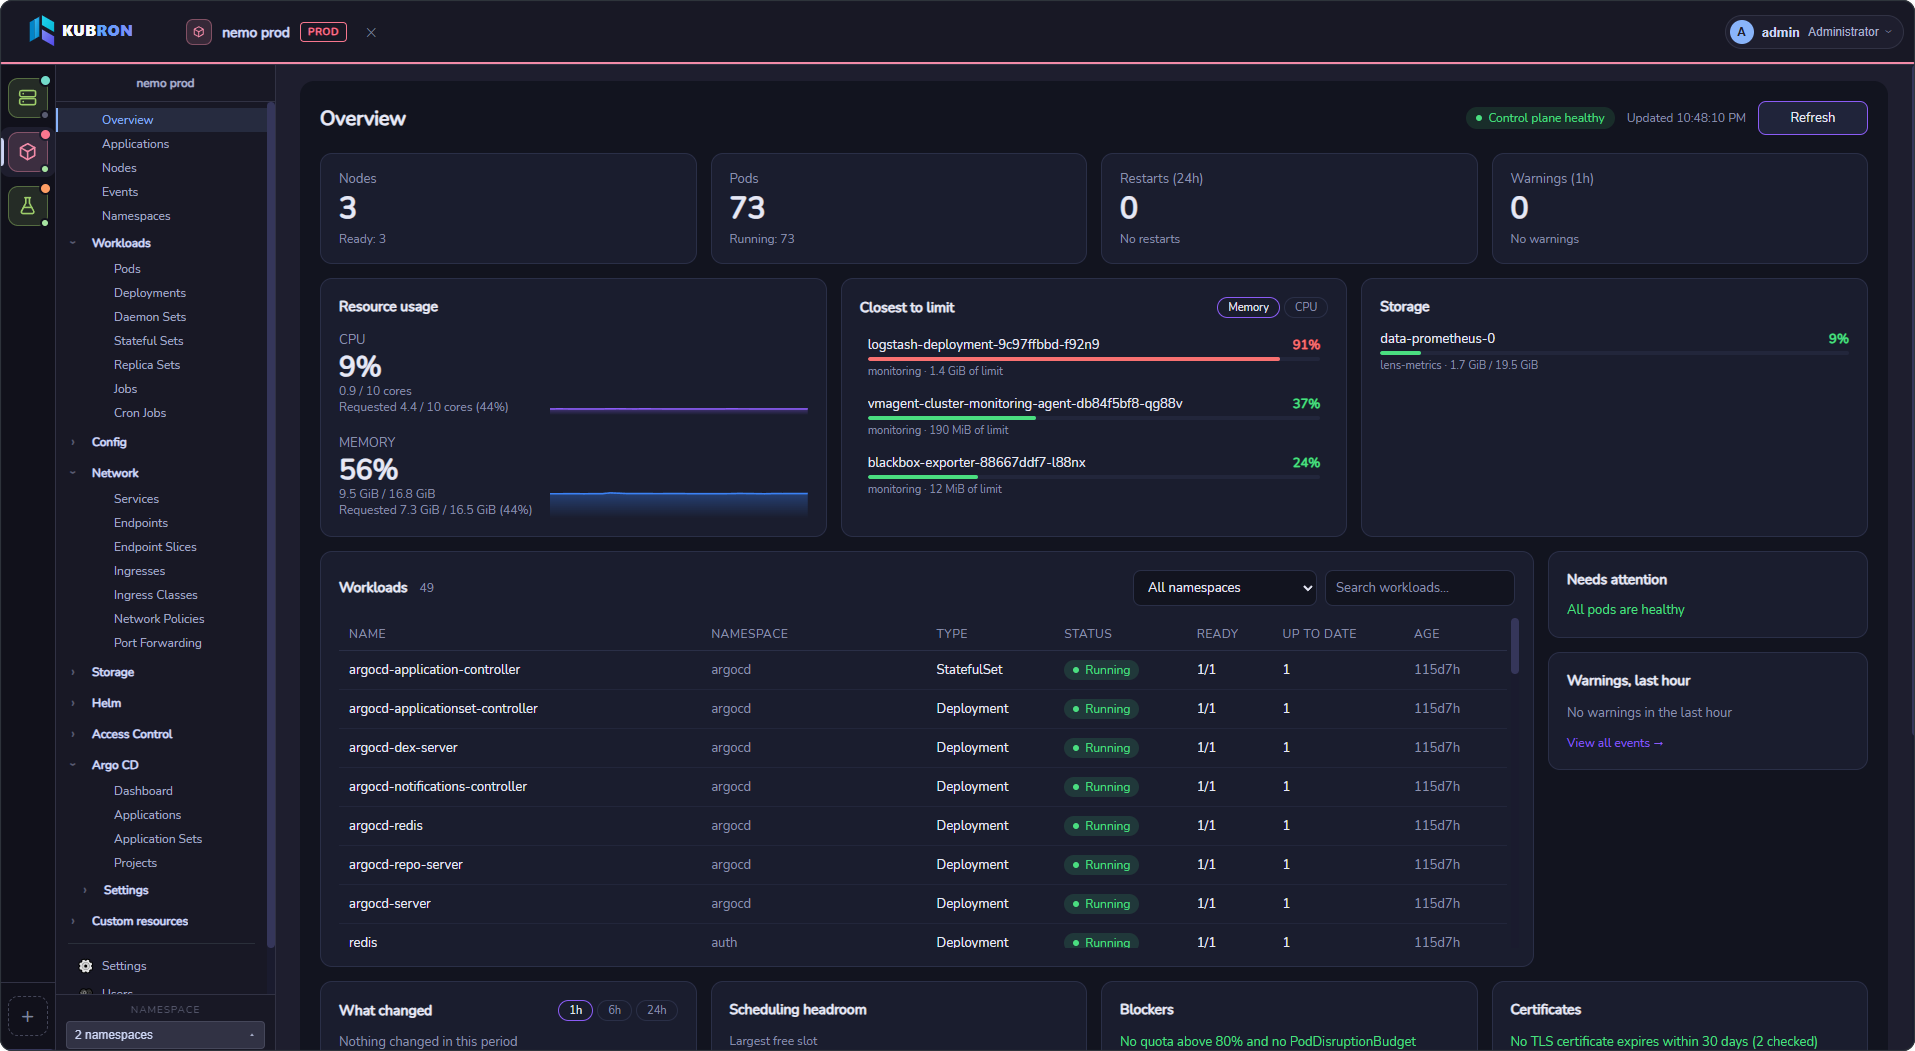
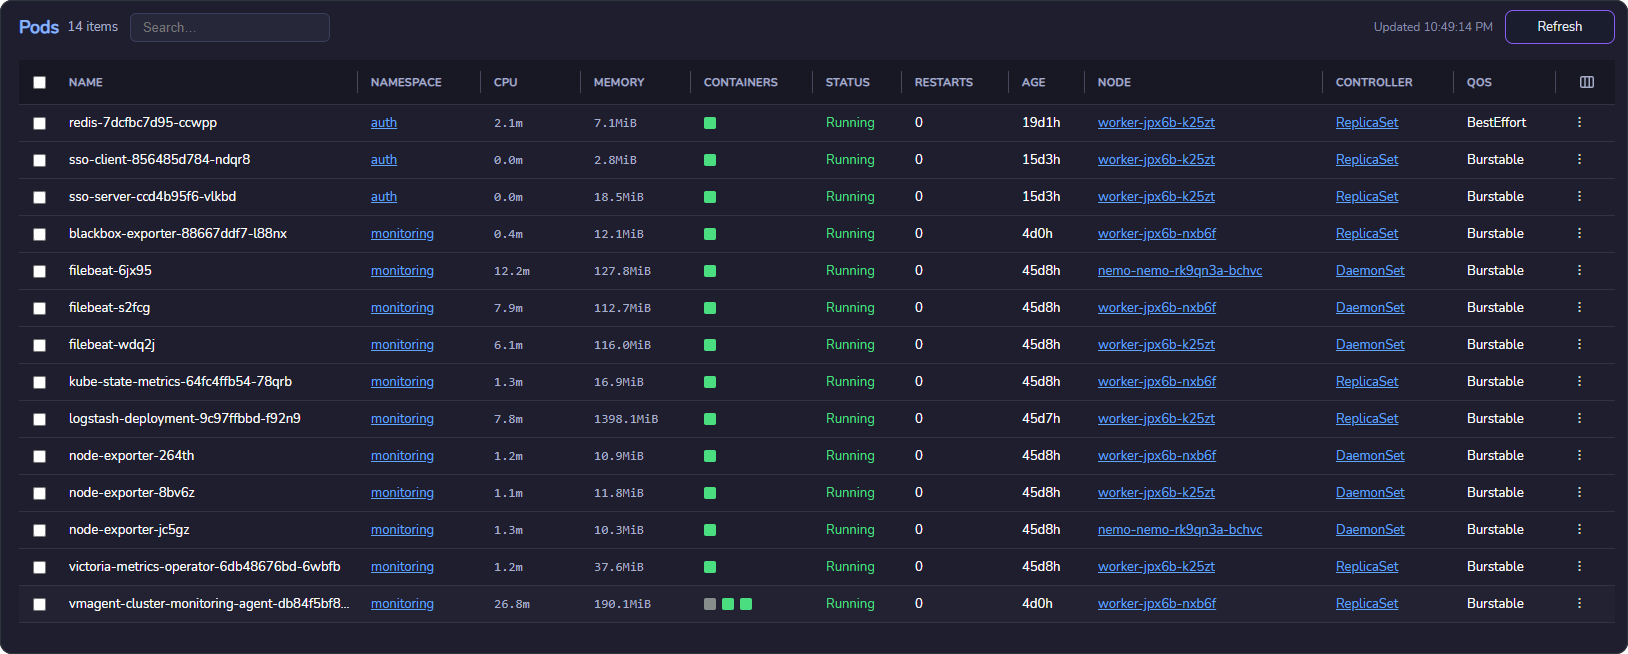
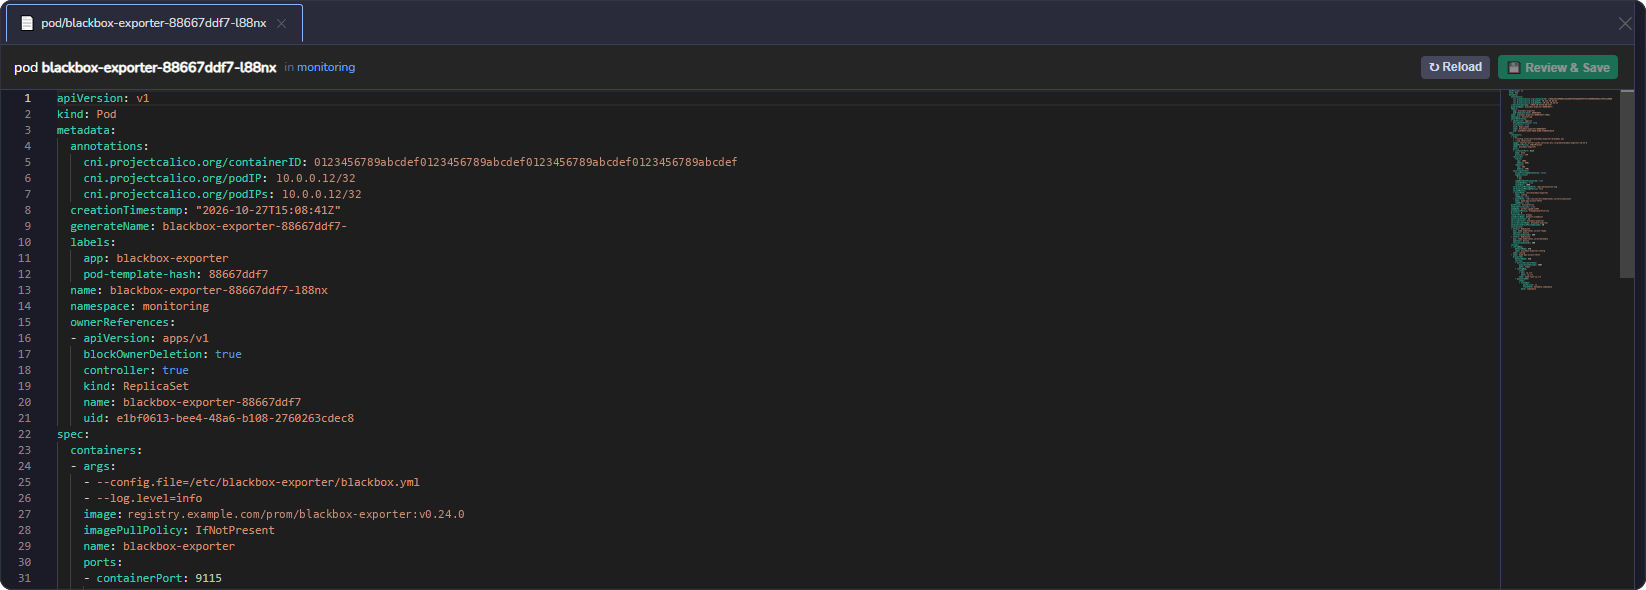
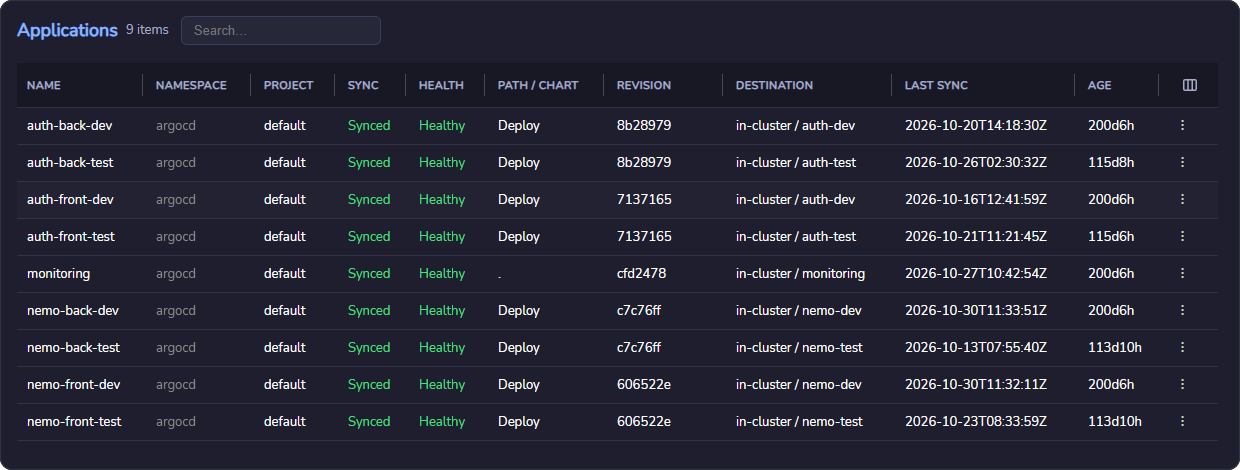
Cluster overview Health, capacity, blockers and recent changes at a glance.Resource browser Inspect pods and workloads, then drill into the details.YAML editor Review the diff before applying a manifest change.GitOps See application health and sync state in context.
Deploy Kubron in your own infrastructure and access it through a browser. Web adds multi-user accounts, roles, permissions and shared state backed by PostgreSQL. It is self-hosted, not a hosted SaaS service.
Multi-cluster workflows — name and color-code clusters, tag environments, and choose one or several namespaces. Restricted RBAC is supported; partial access failures are surfaced.
Live resource views — shared informers keep lists and the dashboard current without aggressive polling.
Light and native. Go plus the system webview: no bundled browser engine, quick to start, easy on memory.
Private by design. No telemetry, no mandatory account, and on Desktop your kubeconfig stays on your machine.
Safe to operate. Environment tags, a mandatory diff before saving YAML, and bulk actions that report failures instead of stopping.
Works with restricted access. Restricted RBAC is a first-class case: no cluster-wide list required.
Signs in to your clusters. OIDC, Azure AKS, AWS EKS and Google GKE are handled natively, and the Web server never runs commands from an uploaded kubeconfig.
Verifiable. Release checksums and provenance, plus signed server images and chart with SBOMs.
Open and multilingual. Apache-2.0, a public extension API, and an interface in English, Русский and 中文.
The desktop application is built with Go, Wails and Vue. Server mode serves the same UI over HTTP for multi-user teams, with PostgreSQL-backed state, encrypted credentials and support for multiple replicas. It is designed to run behind a TLS-terminating reverse proxy.
Desktop does not require an account, sends no telemetry and keeps your kubeconfig on your machine. Web adds local user accounts, fine-grained roles and permissions, session management and an audit log for shared environments.